Joseph Henry Cariazo · security engineering · detection engineering · infrastructure security
10+ years running enterprise infrastructure. Now I attack it and build the detections that catch it.
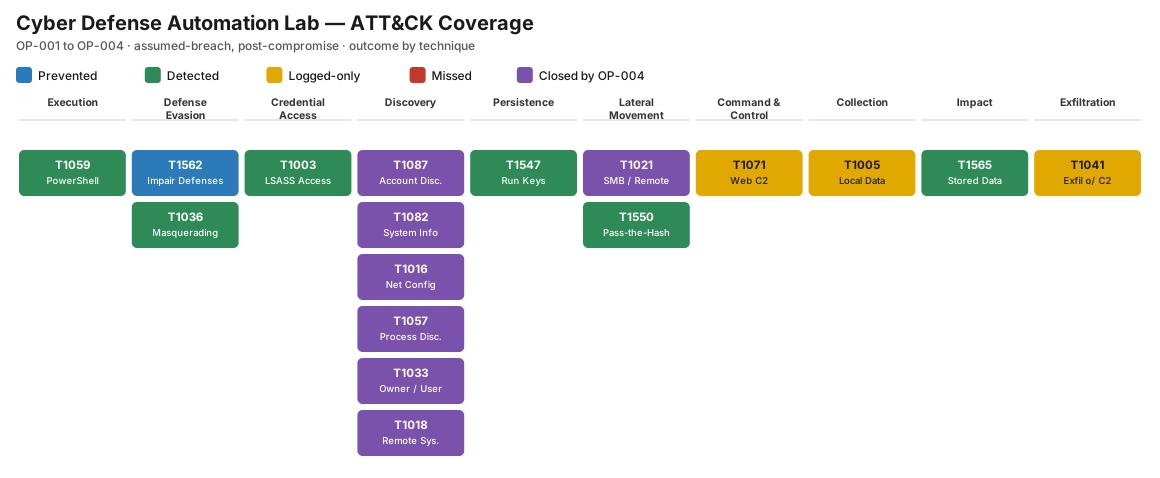
A home SOC built like a small enterprise: an Active Directory domain behind OPNsense and Suricata, with management, target and attack zones separated under default-deny. It’s monitored by Wazuh, Splunk and Sysmon, with n8n, TheHive and MISP for human-approved response. I attack it with MITRE Caldera and Kali, score each step Prevented, Alerted, Logged-only or Missed, turn every miss into a tested detection, and re-run it blind.
The loop, in one picture
flowchart LR
    B[Build<br/>AD lab + SIEM + SOAR] --> A[Attack<br/>Caldera / Kali]
    A --> S[Score every step<br/>Prevented · Alerted ·<br/>Logged-only · Missed]
    S --> D[Detect<br/>turn misses into<br/>tested detections]
    D --> R[Re-run blind<br/>prove the fix]
    R -->|next operation| A
    D --> H[Heartbeat<br/>keep proving it works]
Native discovery · OP-002
Missed → Alerted
Built D1: 4+ discovery tools on one host in 10 min. Caught cold in ~5 min.
Workstation → workstation logon · OP-003
Missed → Alerted
Built D2: logons between peer workstations. Caught cold in ~6 min.
Run-key persistence · OP-001
Logged-only → Alerted
Found why Wazuh was silent; wrote rule 510150. Caught in seconds.
Explore
-
Operations & results
Four assumed-breach operations scored Prevented / Alerted / Logged-only / Missed, then a blind re-run to prove the fixes.
-
Casebook
Incident reports written as a SOC analyst hands off a case: bottom line, timeline, scope, indicators, response, and what changed.
-
Detections as code
Sigma, Wazuh and Splunk rules with must-fire and must-stay-quiet tests that run on every change.
-
SOC tools
EVTX Hunter: triage Windows logs with the same rules, rebuild process trees, and send findings to TheHive.
How the lab is built
Three internal zones (management, monitored endpoints, attacker) plus the WAN uplink, under default-deny, with alerts flowing Wazuh → Splunk and high-severity alerts into n8n for enrichment, a TheHive case and a signed Slack approval before any response.
Stack: Wazuh 4.14 · Splunk 10.4 · Sysmon · OPNsense + Suricata · n8n · TheHive 5 · MISP 2.5 · MITRE Caldera 5.3 · Kali · Active Directory · Windows 10/11 · Ubuntu